Vehicle Data Leak: Privacy, Cybersecurity and Government Data-Sharing Accountability
Revise the static topic: UPSC Polity notes · UPSC Governance notes
In short: The Ministry of Road Transport and Highways has sought a CERT-In forensic security audit of its transport portals after reports that vehicle-linked personal information was being sold through apps and websites. The episode raises questions about whether authentication, masking and contractual restrictions adequately prevent misuse of government-held data by authorised intermediaries.
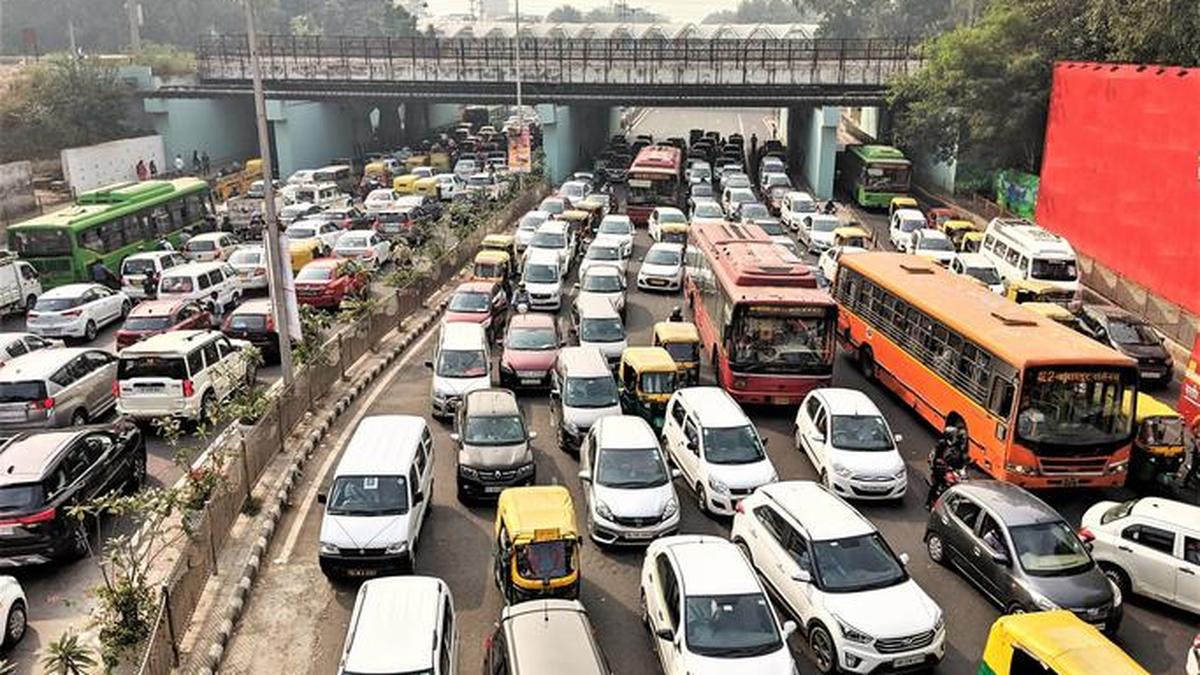
The Ministry of Road Transport and Highways sought a CERT-In forensic audit of its transport portals following reports that vehicle-linked personal information was being sold through apps and websites; the source and mechanism of the reported disclosures remain unproven.
Image: The Hindu
Why in news
MoRTH has asked MeitY to review its data-sharing policy and sought scrutiny of access through the Unified Logistics Interface Platform. It is tightening access controls while retaining data sharing with private entities for legitimate service delivery.
₹5
Reported starting price for vehicle information
25,314
Access credentials issued to private entities
1.708 crore
Queries through private-entity credentials
33 months
Period covered by the reported query total
More than 50 lakh
Monthly hits recorded by many entities accessing ULIP
Background
Transport administration generates linked records concerning vehicles, driving licences, traffic violations and pollution certification. MoRTH’s National Transport Repository consolidates vehicle-registration and driving-licence records alongside data from e-Challans, Detailed Accident Reports and FASTags. Sharing these records can support enforcement and digital services, but linking them to identifiable individuals creates privacy risks. The Supreme Court’s Puttaswamy judgment recognises privacy as a fundamental right, while the Digital Personal Data Protection Act, 2023 provides a statutory framework for processing digital personal data.
What happened and what remains unproven
MoRTH has asked CERT-In to conduct a forensic security audit of VAHAN, SARATHI, e-Challan and PUCC. A Cyderes investigation described a Telegram-based channel offering extensive personal information against a vehicle registration number, including names, addresses, mobile numbers and downloadable documents. The Ministry has also requested major app-store operators to remove such apps.
A preliminary Ministry investigation found evidence of misuse involving ULIP, managed by the National Industrial Corridor Development Corporation. Officials suspect that actors combined information obtained from different portals. These findings warrant investigation, but the source does not establish a final technical cause or prove that the core transport databases were directly hacked.
- A forensic audit should distinguish a direct intrusion from credential abuse, unauthorised onward sharing and misuse of legitimately granted access.
- Unusually high transaction volumes are warning signals, not conclusive proof that every queried record was misused.
- The reported exposure concerns personal information, not merely technical vehicle specifications.
Infographic
Lawful purpose
Specify the legal basis and permitted use.
Minimum disclosure
Share only necessary fields or verification results.
Controlled access
Verify users and apply time-bound permissions.
Continuous oversight
Monitor queries, anomalies and onward sharing.
Enforceable accountability
Investigate misuse, correct failures and enable redress.
AI-assisted infographic by Pragnya IAS Academy, based on the cited sources.
Existing safeguards and the accountability gap
The reported policy permits government bodies, including police and national-security agencies, to access available data fields in accordance with the DPDP Act. Private entities receive selected fields relevant to their domain and face daily search limits. Access is provided through APIs or login-based arrangements, with controls including secret keys, two-factor authentication and Aadhaar-authenticated OTPs.
Personally identifiable information is masked except for law-enforcement and security agencies, and the policy requires entities to possess a Security Audit Certificate from CERT-In. Nevertheless, authentication establishes who is accessing a system; it does not by itself establish that every query serves an authorised purpose. Similarly, masking can be undermined when records are linked with other datasets.
- Access permissions must be limited by purpose, data field, role and duration.
- Security certification should be supplemented by continuous monitoring of actual behaviour.
- Data recipients must remain accountable for retention, onward sharing and misuse of credentials.
- Enforcement agencies require oversight as well as private intermediaries.
Constitutional privacy and statutory responsibility
Informational privacy is protected within the constitutional right to privacy, including under Article 21. State interference must satisfy requirements of legality, legitimate aim and proportionality, supported by safeguards against abuse. The ability to collect transport information for registration or enforcement does not create an unlimited entitlement to disclose it for unrelated purposes.
The DPDP Act provides for obligations concerning lawful processing, reasonable security safeguards and personal-data-breach intimation within its statutory framework. However, the supplied report does not establish which provisions or implementing requirements were operational at the time. Specific liability must therefore be assessed against the applicable legal position and the forensic findings.
Consent is not the sole basis for every lawful State processing activity. Equally, public ownership of a database does not make its contents unrestricted public information. Government data-sharing policies must be evaluated alongside constitutional requirements and applicable statutory duties.
- Purpose limitation restricts processing to the authorised objective.
- Data minimisation reduces the personal information exposed for a particular service.
- Privacy protection must extend across collection, access, storage, onward disclosure and deletion.
The policy response: preserve utility, constrain misuse
Through an October 19 letter, MoRTH asked NIC to audit ULIP users’ access and usage patterns against approved purposes and terms. It separately sought information from NICDC’s data services arm on eligibility screening, due diligence, access scope and monitoring. The Ministry also plans to audit enforcement agencies accessing its portals.
Following an Internet Freedom Foundation representation, MoRTH has tightened technical controls and will limit ULIP data sharing. Government agencies seeking data will require Transport Secretary approval, while requesting officers must be verified through an Aadhaar-based digital signature certificate or video KYC. Officials have ruled out suspending private-sector sharing altogether.
The policy challenge is therefore not a binary choice between open access and complete shutdown. A defensible model combines narrowly defined access, auditable purposes, anomaly detection and effective sanctions without obstructing legitimate public services.
- Senior approval establishes responsibility but cannot substitute for monitoring individual queries.
- Identity verification should be paired with checks on the necessity and scope of each access entitlement.
- Restrictions should target demonstrated risks while preserving justified service continuity.
| Platform or institution | Role |
|---|---|
| VAHAN | Manages vehicle-registration records. |
| SARATHI | Handles driving licences and related services. |
| e-Challan | Records traffic violations and fines. |
| PUCC | Manages pollution control certificates. |
| National Transport Repository | Consolidates transport records and associated datasets for policy-governed access. |
| ULIP | Unified Logistics Interface Platform, managed by NICDC; its data-access arrangements are under scrutiny. |
| CERT-In | National cyber incident response agency asked to conduct the forensic security audit. |
| NIC | National Informatics Centre, asked to audit ULIP users’ access and usage patterns. |
- 1. Establish the legal basis, service purpose and minimum data required.
- 2. Verify the requesting entity and responsible officers through documented due diligence.
- 3. Grant time-bound, least-privilege access with field restrictions and query limits.
- 4. Log queries and monitor volumes, patterns and purpose compliance.
- 5. Investigate anomalies, preserve evidence and restrict suspect access where justified.
- 6. Enforce corrective action, deletion requirements and applicable notification and redress duties.
2017
The Supreme Court’s Puttaswamy judgment recognises privacy as a fundamental right.
2023
The Digital Personal Data Protection Act is enacted.
October 19, as reported
MoRTH writes to NIC seeking an audit of ULIP users’ access and usage against approved purposes and terms.
Significance, challenges & way forward
Significance
- Government-held transport records can connect an ordinary vehicle registration number to an individual’s identity and address.
- The episode highlights that cybersecurity includes misuse by authorised users, not only attacks by outsiders.
- Secure data sharing supports digital services and legitimate business activity without treating personal information as an unrestricted commodity.
- Auditing public agencies alongside private recipients strengthens accountability across the entire access chain.
- Trust in digital governance depends on whether citizens can rely on the State to control downstream uses of their information.
Challenges
- Combining records from multiple portals may reveal identities despite masking within an individual dataset.
- Large numbers of credentials complicate ownership checks, periodic review and timely revocation.
- High transaction volumes can reflect either legitimate demand or abuse, requiring contextual investigation rather than automatic conclusions.
- Responsibilities may become fragmented among the database custodian, platform operator, recipient entity and downstream service provider.
- App removal may reduce immediate availability without eliminating copied datasets or alternative distribution channels.
- Certification and senior-level approvals can become procedural formalities unless linked to continuous monitoring and enforceable consequences.
Way forward
- Complete a coordinated forensic investigation that reconstructs access paths, preserves evidence and separates confirmed findings from suspicions.
- Maintain a verified register of recipients, credentials, approved purposes, permitted fields and access-expiry dates.
- Use risk-based query thresholds and alerts for bulk extraction, unusual access patterns and repeated searches unrelated to approved services.
- Prefer limited verification responses over disclosure of complete personal records wherever the service permits.
- Require recipients to document retention, deletion and onward-sharing practices, supported by audit rights and consequences for violations.
- Publish a non-sensitive summary of findings and corrective measures without exposing personal information or exploitable vulnerabilities.
- Provide accessible grievance and incident-response channels, with notifications and remedies consistent with applicable law.
Key terms
- Forensic security audit
- An evidence-based examination of systems and logs to reconstruct an incident, determine its scope and identify control failures.
- Personally identifiable information
- Information that identifies, or can help identify, an individual directly or through linkage.
- Application programming interface
- A defined interface through which software systems exchange requests and data.
- Purpose limitation
- Restricting data processing and access to specified, authorised objectives.
- Data minimisation
- Limiting personal data collected or disclosed to what is necessary for the intended purpose.
- Least privilege
- Granting a user or system only the access necessary to perform an authorised task.
- Data triangulation
- Combining information from multiple sources to infer or assemble additional details about an individual.
- Data masking
- Concealing identifiable fields in a dataset without necessarily making re-identification impossible.
Link with static syllabus
Prelims practice MCQs
Q1. Consider the following pairs: 1. VAHAN: Vehicle-registration records 2. SARATHI: Driving licences and related services 3. PUCC: Traffic violations and fines Which of the pairs given above are correctly matched?
Q2. With reference to safeguards for government data sharing, consider the following statements: 1. Two-factor authentication by itself establishes that every query serves an authorised purpose. 2. Masked data may become identifiable when combined with other datasets. 3. Least-privilege access limits permissions to what is necessary for an authorised task. Which of the statements given above are correct?
Q3. Which institution has MoRTH asked to conduct a forensic security audit of VAHAN, SARATHI, e-Challan and PUCC?
Q4. With reference to informational privacy in India, consider the following statements: 1. The Puttaswamy judgment recognised privacy as a fundamental right. 2. Personal information held by a government database automatically becomes unrestricted public information. 3. State interference with privacy must satisfy constitutional requirements, including legality and proportionality. Which of the statements given above are correct?
Mains practice questions
GS 2 · 15 marks · 250 words
Government data sharing must balance service-delivery gains with informational privacy and cybersecurity accountability. Discuss in the context of the reported vehicle-data leak.
Frequently asked questions
Was the reported vehicle-data leak necessarily caused by hacking?
The source does not establish a final technical cause. The investigation must distinguish direct intrusion from credential misuse, unauthorised onward sharing and aggregation of data from multiple portals.
Has MoRTH stopped sharing data with private entities?
No. Officials ruled out suspending private-sector sharing altogether, while announcing tighter controls and limits on ULIP data sharing.
Why are masking and two-factor authentication not sufficient?
Masking may be undermined by linking datasets, while two-factor authentication does not establish that an authenticated user is acting within the approved purpose. Both require support from restricted permissions, monitoring and enforcement.
What is the main UPSC governance takeaway?
Government data sharing requires accountability throughout the access chain, not merely security at the central database. Privacy, service delivery and cybersecurity must be addressed together through proportionate safeguards.
Sources
Analysis prepared by the Pragnya IAS Academy current-affairs desk with AI assistance from the cited reports. Verify figures with the original sources.
Turn current affairs into marks
Join Pragnya IAS Academy's mentorship for daily answer-writing evaluation on stories like this — classroom programmes from a trusted name in IAS coaching in Hyderabad.